
One of the more unusual upgrade blockers I've worked through was an environment that was completely healthy.
The problem was the architecture.
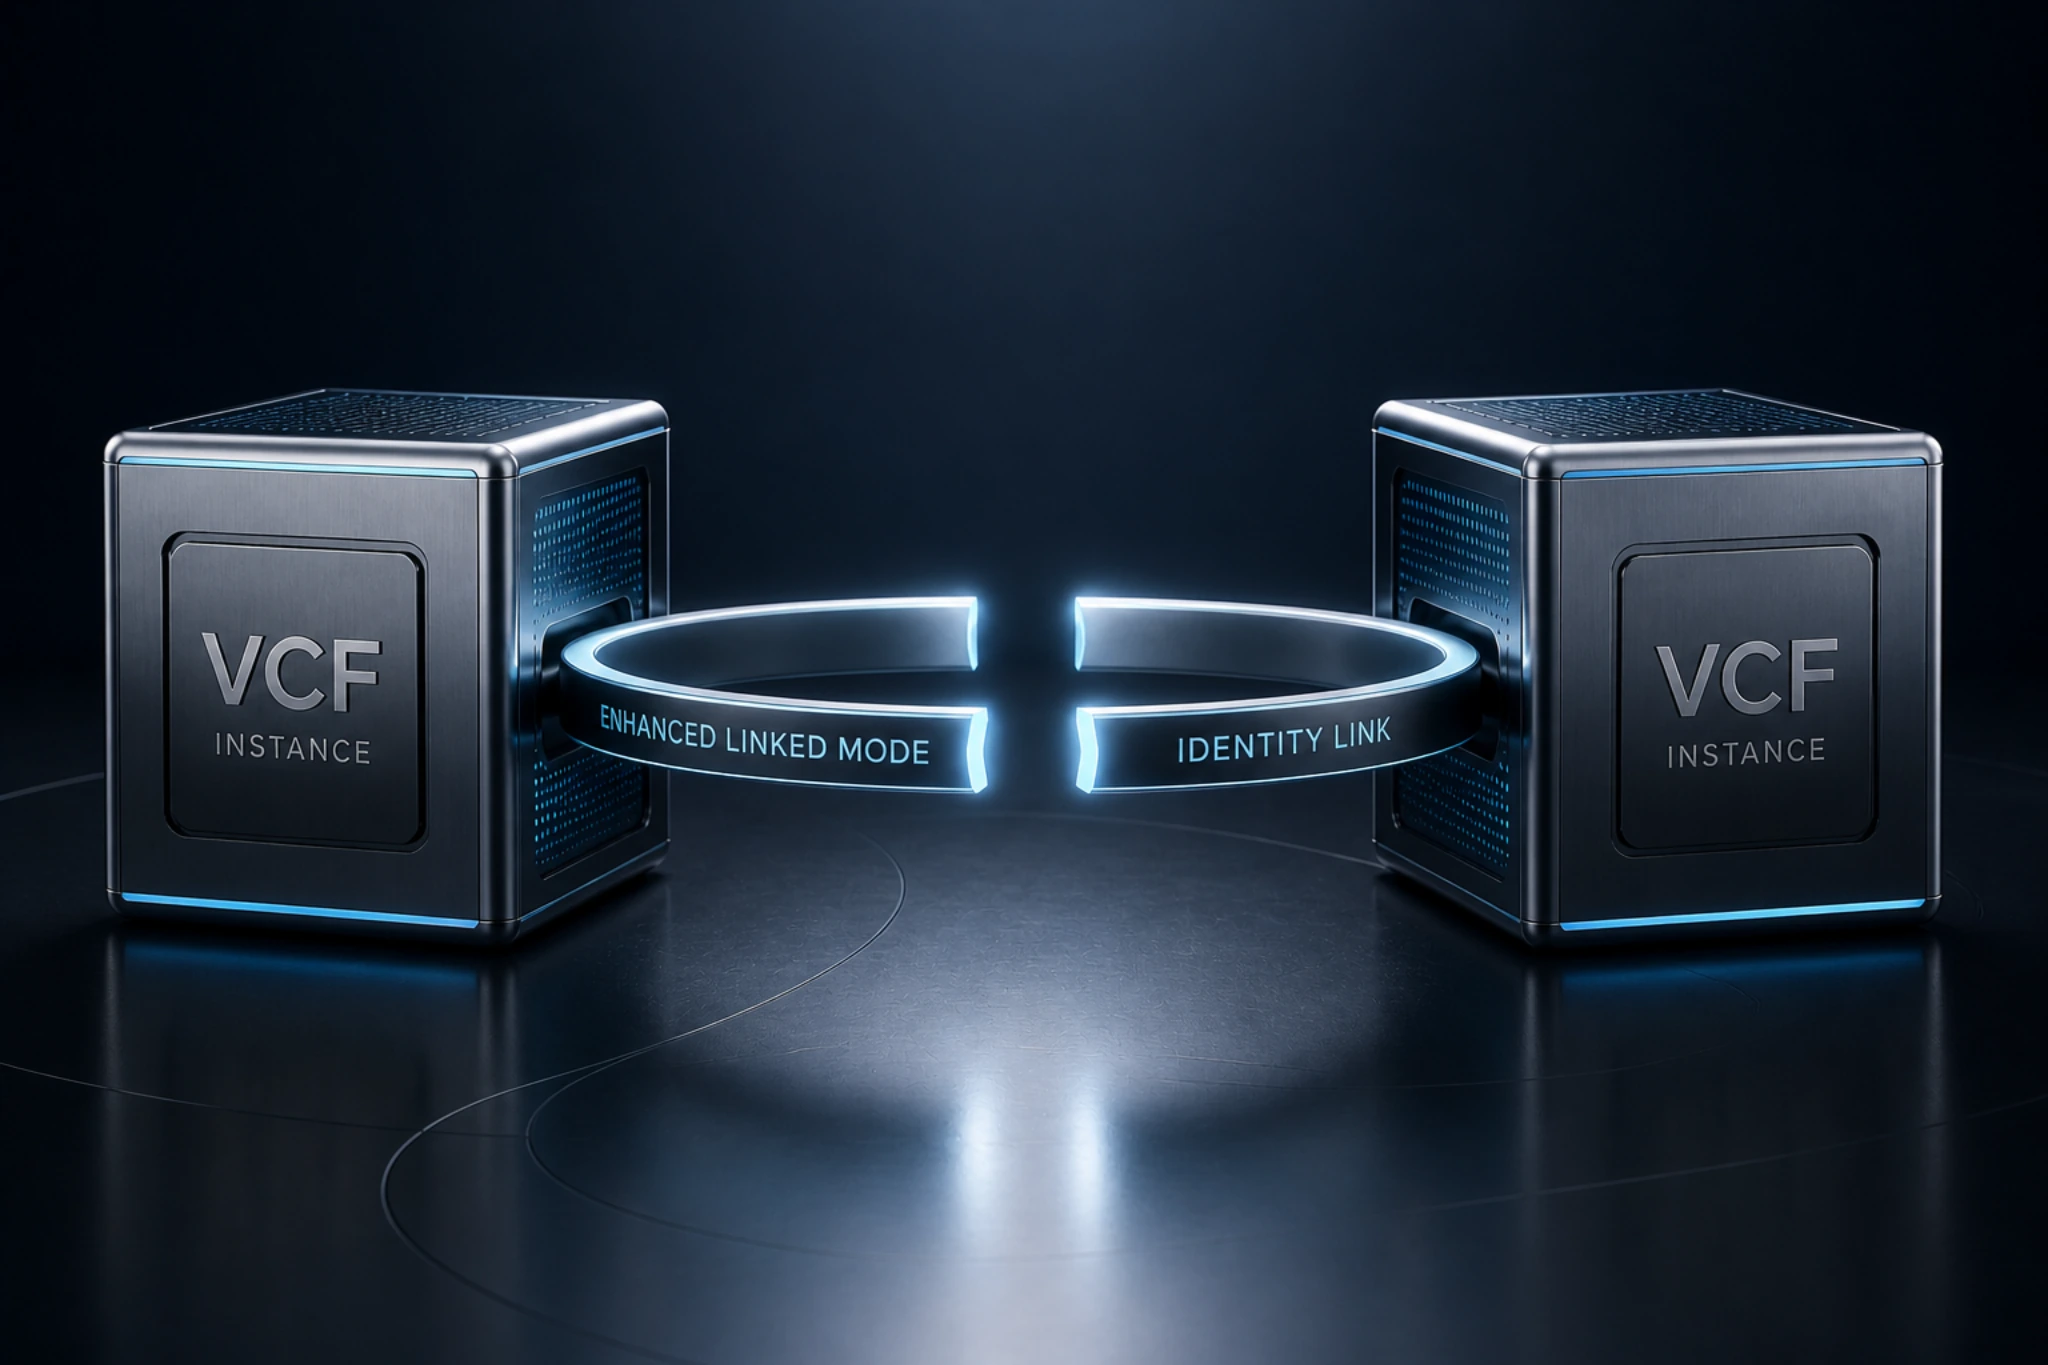
Two separate VCF instances were still joined through Enhanced Linked Mode and a shared SSO/vmdir topology. That design had been put in place when it was supported and it continued to work, but by the time we needed to move forward with the upgrade it had become something we had to unwind first.
I wrote up what we ran into here:
 www.vcfinsider.com
Breaking the relationship turned out to be a lot more than unlinking a couple of vCenters. We had to think about SSO membership, vmdir replication, the replication topology after the split, certificates, rollback, and the cleanup that was still left once the main work was done.
That whole change was a good reminder that "it works" and "it's a good place to start the next upgrade" are not always the same thing.
I'd be interested to hear from anyone else who has had to separate an older ELM or shared-SSO design. What ended up being the part you worried about most, and what did you find after the split that you hadn't planned for?
I'd also be careful with commands from somebody else's environment here. This is one of those changes where I'd want to understand the exact topology before touching anything.
The problem was the architecture.
Two separate VCF instances were still joined through Enhanced Linked Mode and a shared SSO/vmdir topology. That design had been put in place when it was supported and it continued to work, but by the time we needed to move forward with the upgrade it had become something we had to unwind first.
I wrote up what we ran into here:
Breaking ELM Between Two VCF Instances to Restore a Supported Upgrade Path
A real-world VMware Cloud Foundation field note on breaking a cross-instance Enhanced Linked Mode topology.
www.vcfinsider.com
Breaking the relationship turned out to be a lot more than unlinking a couple of vCenters. We had to think about SSO membership, vmdir replication, the replication topology after the split, certificates, rollback, and the cleanup that was still left once the main work was done.
That whole change was a good reminder that "it works" and "it's a good place to start the next upgrade" are not always the same thing.
I'd be interested to hear from anyone else who has had to separate an older ELM or shared-SSO design. What ended up being the part you worried about most, and what did you find after the split that you hadn't planned for?
I'd also be careful with commands from somebody else's environment here. This is one of those changes where I'd want to understand the exact topology before touching anything.